Published: September 2026 | Technical Risk & Insurance Strategy Guide
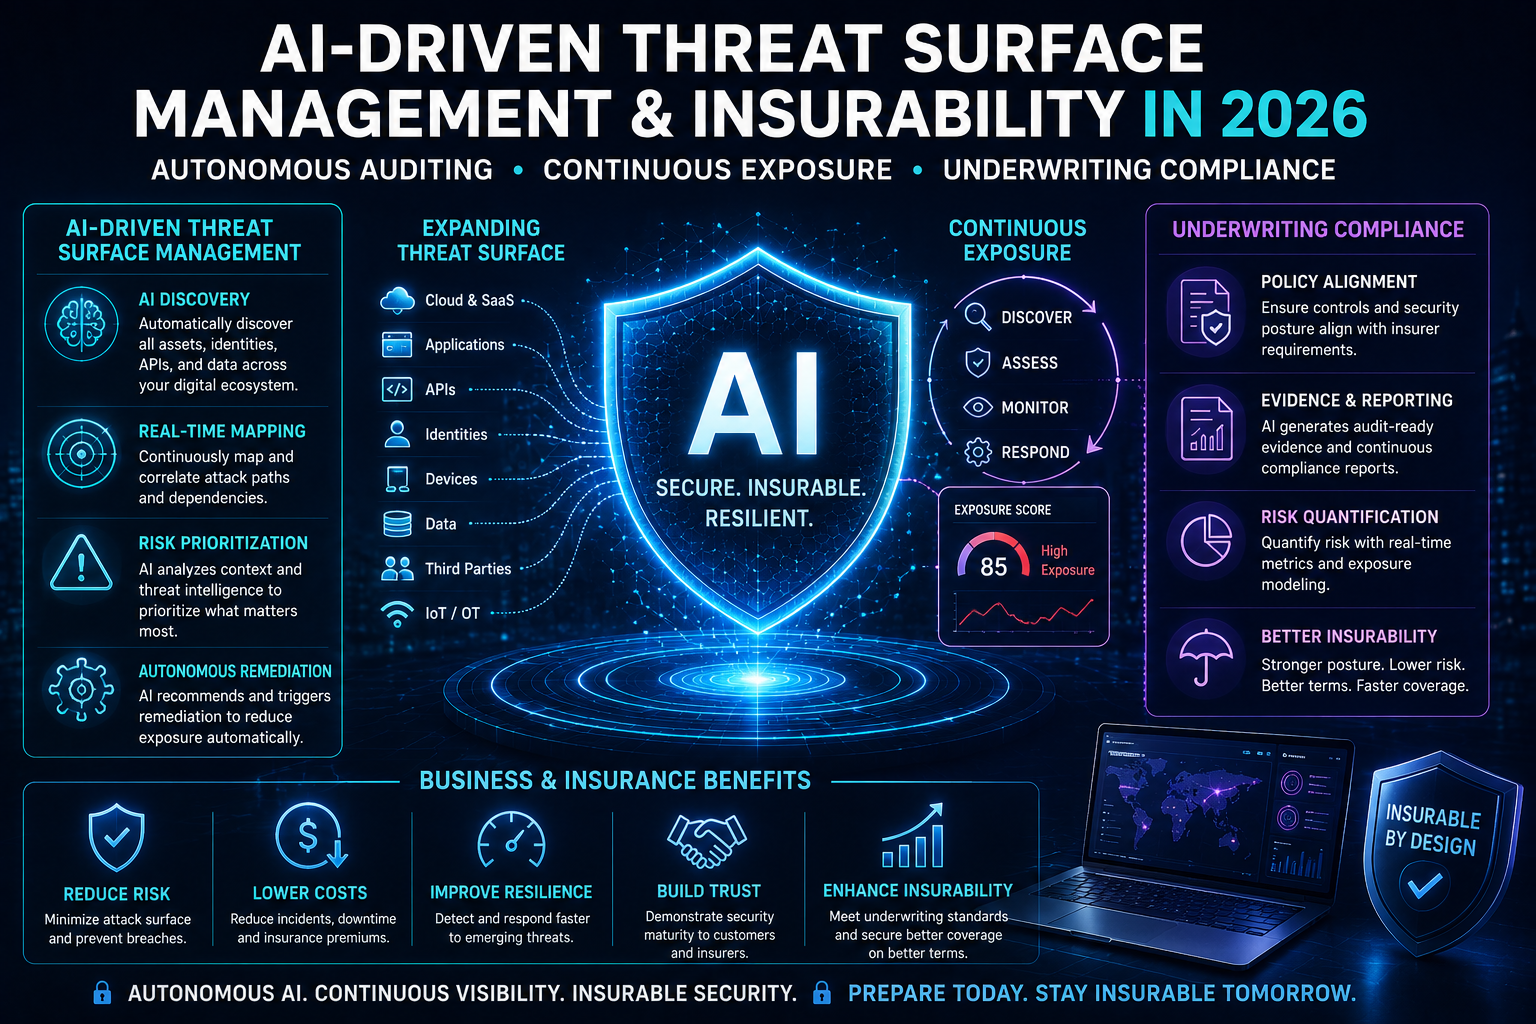
As enterprise attack surfaces expand across multi-cloud environments, remote endpoints, and dynamic API integrations, traditional static risk assessments and annual vulnerability scans are no longer sufficient for cyber insurance underwriting. Threat actors are leveraging automated, AI-driven reconnaissance tools to identify and exploit zero-day vulnerabilities within hours of exposure.
To maintain insurable status and secure high-limit coverage, organizations are migrating toward Continuous Threat Exposure Management (CTEM) and Autonomous Attack Surface Management (AASM) frameworks. Insurance carriers now prioritize real-time telemetry, automated asset discovery, and verified exposure management over point-in-time questionnaires.
This technical guide details how AI-driven threat surface management impacts cyber insurance underwriting, the key metrics carriers evaluate, and the steps required to achieve compliance.
The Evolving Threat Landscape: Static Audits vs. Continuous Monitoring
Traditional cyber underwriting relied heavily on yearly security assessments. However, rapid cloud deployments and shadow IT have made static audits obsolete.
Static Vulnerability Scans:
- Conducted annually or quarterly, leaving wide coverage gaps between scans.
- High rate of false positives without contextual prioritization.
- Fails to detect real-time configuration drift across cloud environments.
AI-Driven Attack Surface Management (AASM):
- Continuous discovery of active, shadow, and unmanaged assets.
- Context-aware threat prioritization using machine learning models.
- Real-time integration with underwriting telemetry systems.
Underwriting Compliance Baseline: What Insurance Carriers Expect
Insurers now demand proof that enterprise security controls adapt dynamically to emerging vulnerabilities:
| Compliance Area | Legacy Requirement | 2026 Underwriting Standard |
| Asset Discovery | Manual inventory spreadsheets | Automated, continuous CBOM & asset mapping |
| Vulnerability Patching | 30-to-90-day patch SLA | Contextual remediation within 24–72 hours for critical CVEs |
| Cloud Security Posture | Periodic cloud configuration checks | Real-time posture management (CSPM) with automated guardrails |
| Third-Party Risk | Vendor questionnaires | Continuous supply-chain exposure monitoring |
Anatomy of Policy Terms & Exclusions for Unmanaged Exposure
Insurers are introducing specific endorsements and exclusions targeting unmanaged digital assets:
- Unpatched Known Exploited Vulnerabilities (KEV) Exclusion: Denies or limits coverage for breaches stemming from vulnerabilities listed on public registries (e.g., CISA KEV) that remained unpatched past mandatory SLAs.
- Shadow IT & Undisclosed Infrastructure Limits: Sub-limits or restricted payouts for incidents originating from unmanaged cloud accounts or unauthorized third-party integrations.
- Continuous Monitoring Premium Discounts: Affirmative coverage incentives and premium reductions for enterprises sharing live telemetry feeds via security API integrations with underwriters.
Case Scenarios: Exposure Management & Claim Outcomes
Scenario A: Claim Denial Due to Unmanaged Cloud Instance
- The Incident: An unmonitored development server containing customer record backups was exposed to the public internet during a cloud migration. Attackers extracted the data within 48 hours.
- The Insurance Outcome: The carrier denied full policy limits under the “Unmanaged Infrastructure Exclusion,” as the asset was absent from the company’s submitted asset inventory during renewal.
Scenario B: Premium Reduction via Continuous Telemetry
- The Incident: A fintech company integrated automated AASM software into its security operations, providing verified real-time vulnerability tracking to its insurer.
- The Insurance Outcome: Upon annual renewal, the company secured a 12% premium discount and full coverage limits for zero-day exploitation risks.
The CISO Action Plan for AASM Compliance
To meet modern underwriting expectations and streamline insurance renewals, security leaders should implement the following lifecycle:
- Deploy Autonomous Asset Discovery: Implement agentless scanning tools to map all internet-facing assets, APIs, and cloud resources across the enterprise.
- Establish Risk-Based Prioritization: Use AI models to correlate vulnerability severity with asset criticality, ensuring security teams focus on high-impact risks first.
- Automate Patch Verification: Validate that critical security patches are deployed and verified automatically within vendor-defined exposure windows.
- Share Verified Audit Logs: Provide underwriters with continuous compliance reports and real-time posture scoring to negotiate optimal policy terms.
Frequently Asked Questions (FAQs)
What is Continuous Threat Exposure Management (CTEM)?
CTEM is a structured security framework that continuously discovers, prioritizes, and validates enterprise threat exposures, replacing traditional annual penetration testing.
How do underwriters view shadow IT?
Underwriters view shadow IT as an unquantified risk. Unmonitored assets often fall under specific policy exclusions or sub-limits if they lead to a security breach.
Can real-time security telemetry reduce insurance costs?
Yes. Many leading cyber insurance carriers offer lower deductibles, higher limits, and premium discounts for enterprises that share continuous, automated security data.