Quantum Insurance Risk: How CISOs Must Prep for the Post-RSA Era
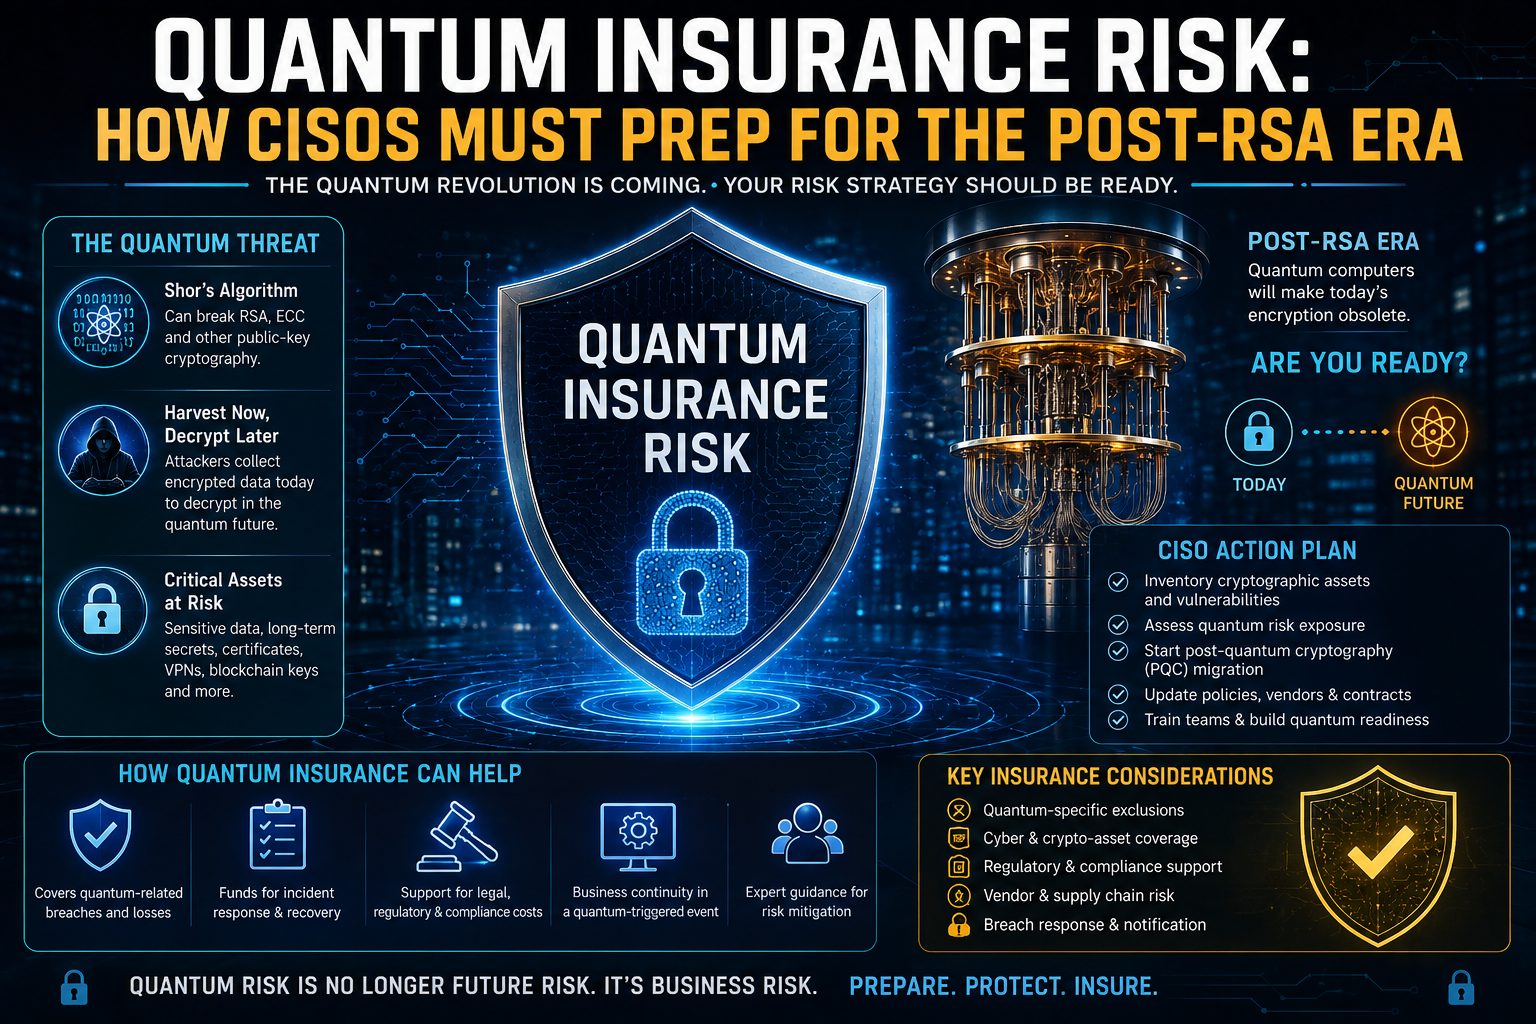
Abstract representation of quantum cryptography protecting corporate data assets.

Published: September 2026 | Enterprise Security & Cyber Insurance Briefing The threat of quantum computing breaking modern encryption isn’t a future scenario—it’s an operational risk affecting cyber insurance policies today. Adversaries are actively gathering encrypted corporate data via “Harvest Now, Decrypt Later” (HNDL), creating massive future breach liabilities for enterprises. As underwriters adjust their policies, … Read more
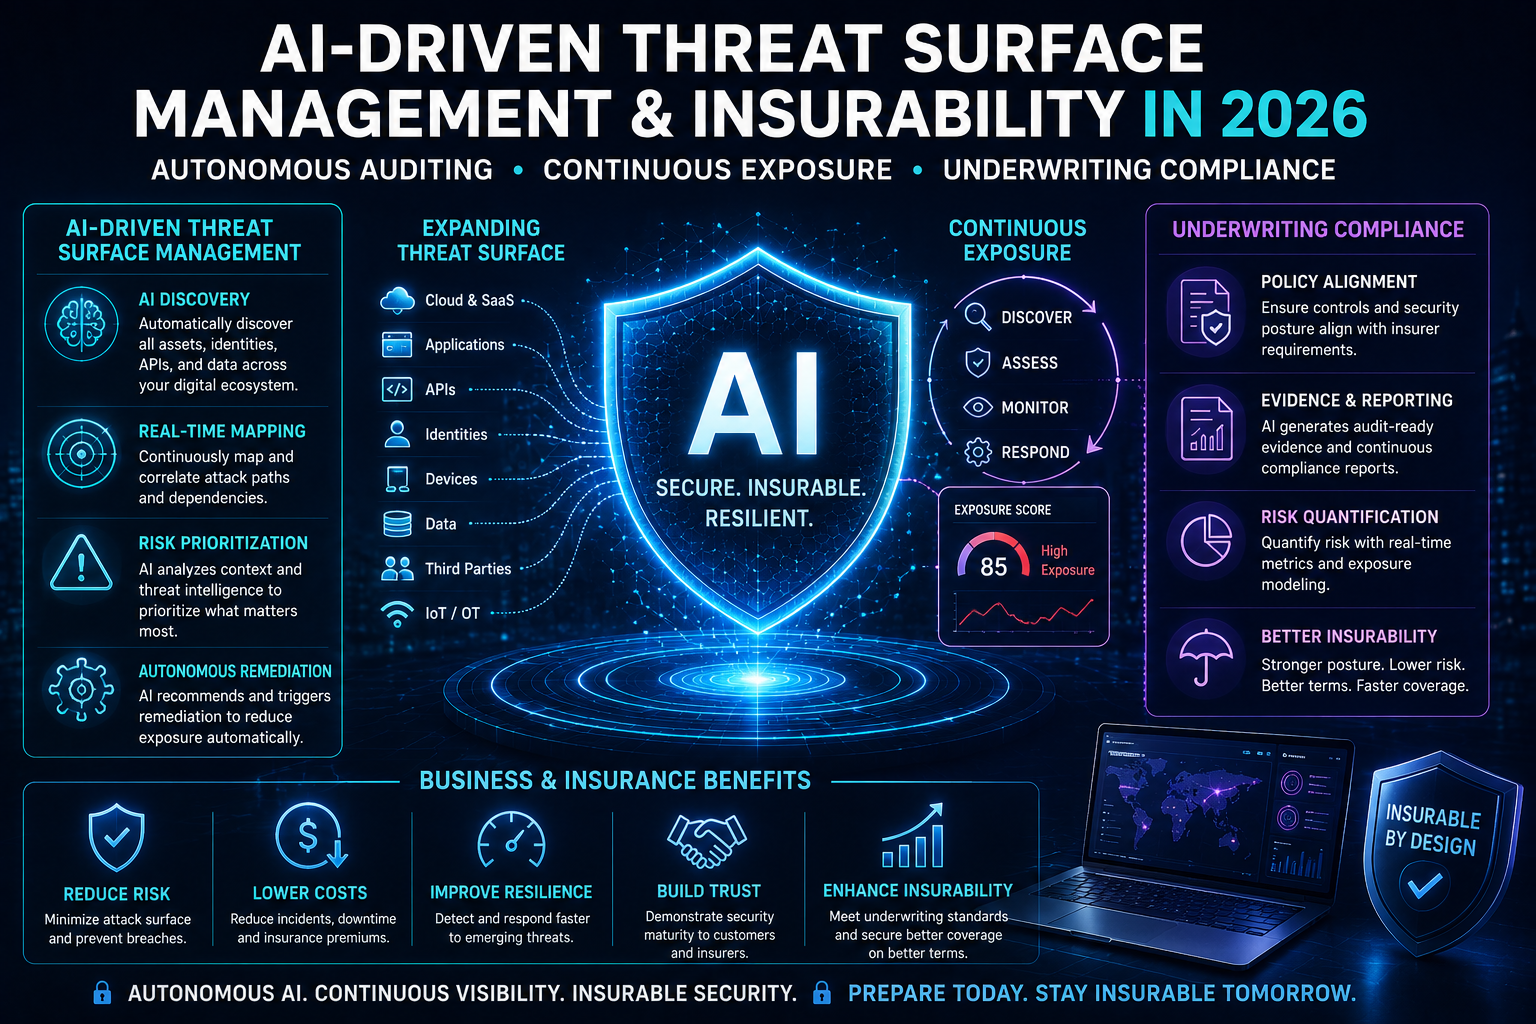
AI-Driven Threat Surface Management & Insurability in 2026: Autonomous Auditing, Continuous Exposure, & Underwriting Compliance

Digital representation of AI-driven attack surface management dashboard monitoring corporate network nodes.

Published: September 2026 | Technical Risk & Insurance Strategy Guide As enterprise attack surfaces expand across multi-cloud environments, remote endpoints, and dynamic API integrations, traditional static risk assessments and annual vulnerability scans are no longer sufficient for cyber insurance underwriting. Threat actors are leveraging automated, AI-driven reconnaissance tools to identify and exploit zero-day vulnerabilities within … Read more

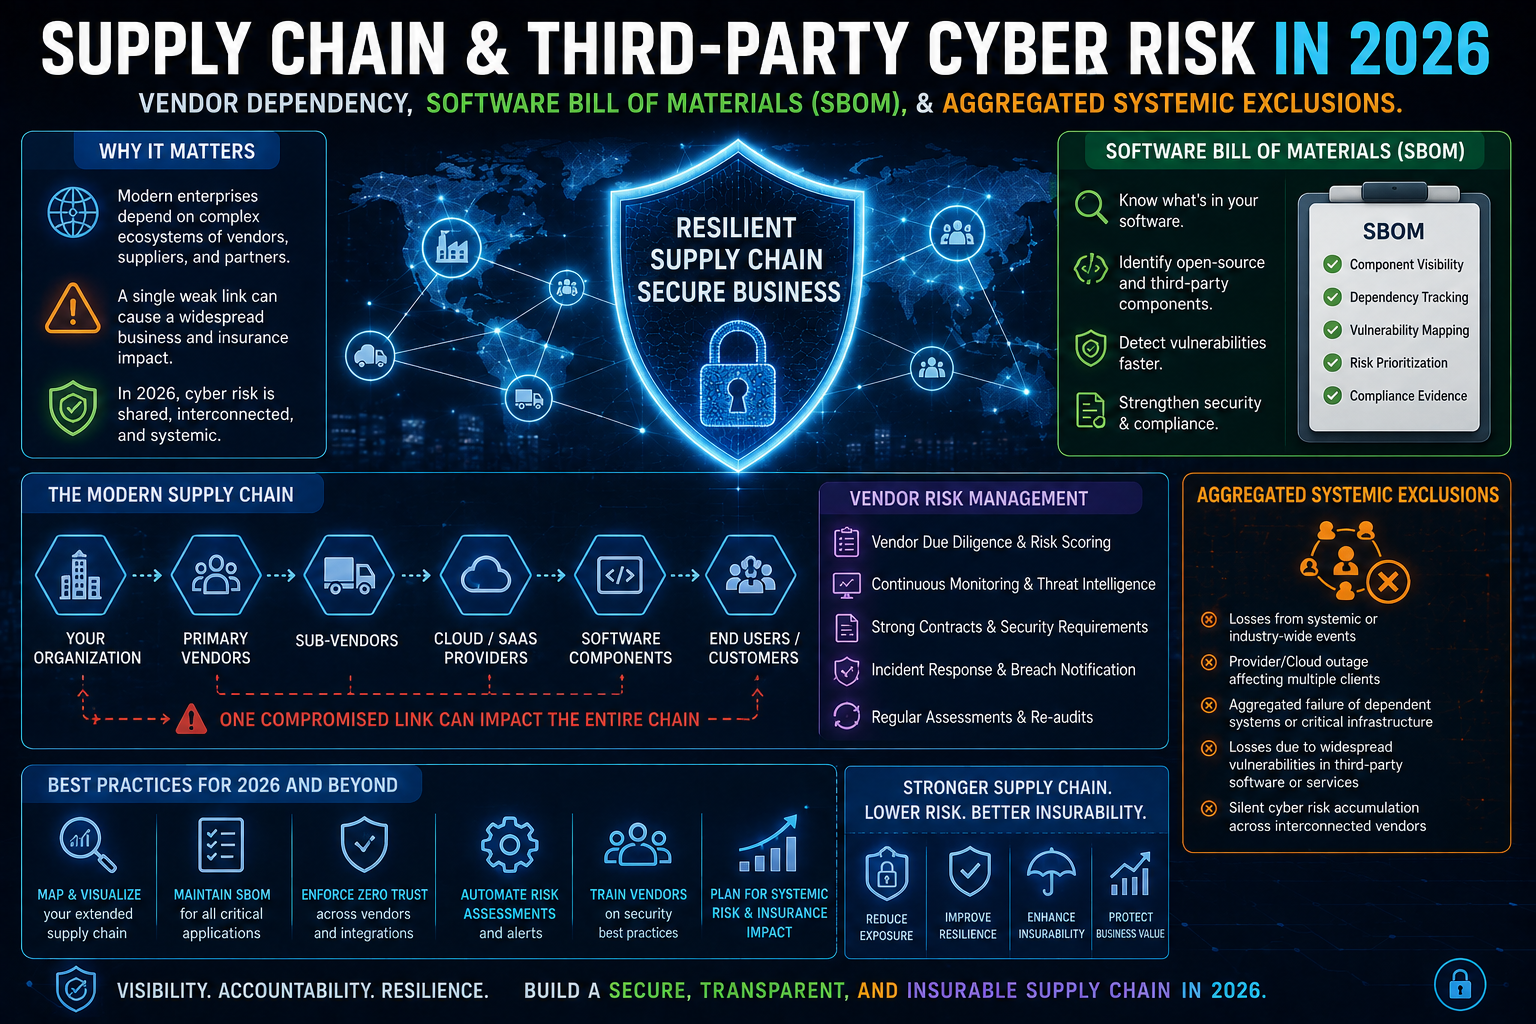
Supply Chain & Third-Party Cyber Risk in 2026: Vendor Dependency, Software Bill of Materials (SBOM), & Aggregated Systemic Exclusions

Conceptual digital visual representing digital supply chain security, software bill of materials, and vendor risk management.

Published: September 2026 | Technical Risk & Insurance Strategy Guide Modern enterprises rely heavily on vast networks of cloud providers, managed service providers (MSPs), SaaS platforms, and third-party software libraries. While this ecosystem accelerates operational efficiency, it also introduces severe supply chain vulnerabilities. A single breach at a critical vendor can trigger cascading security failures … Read more

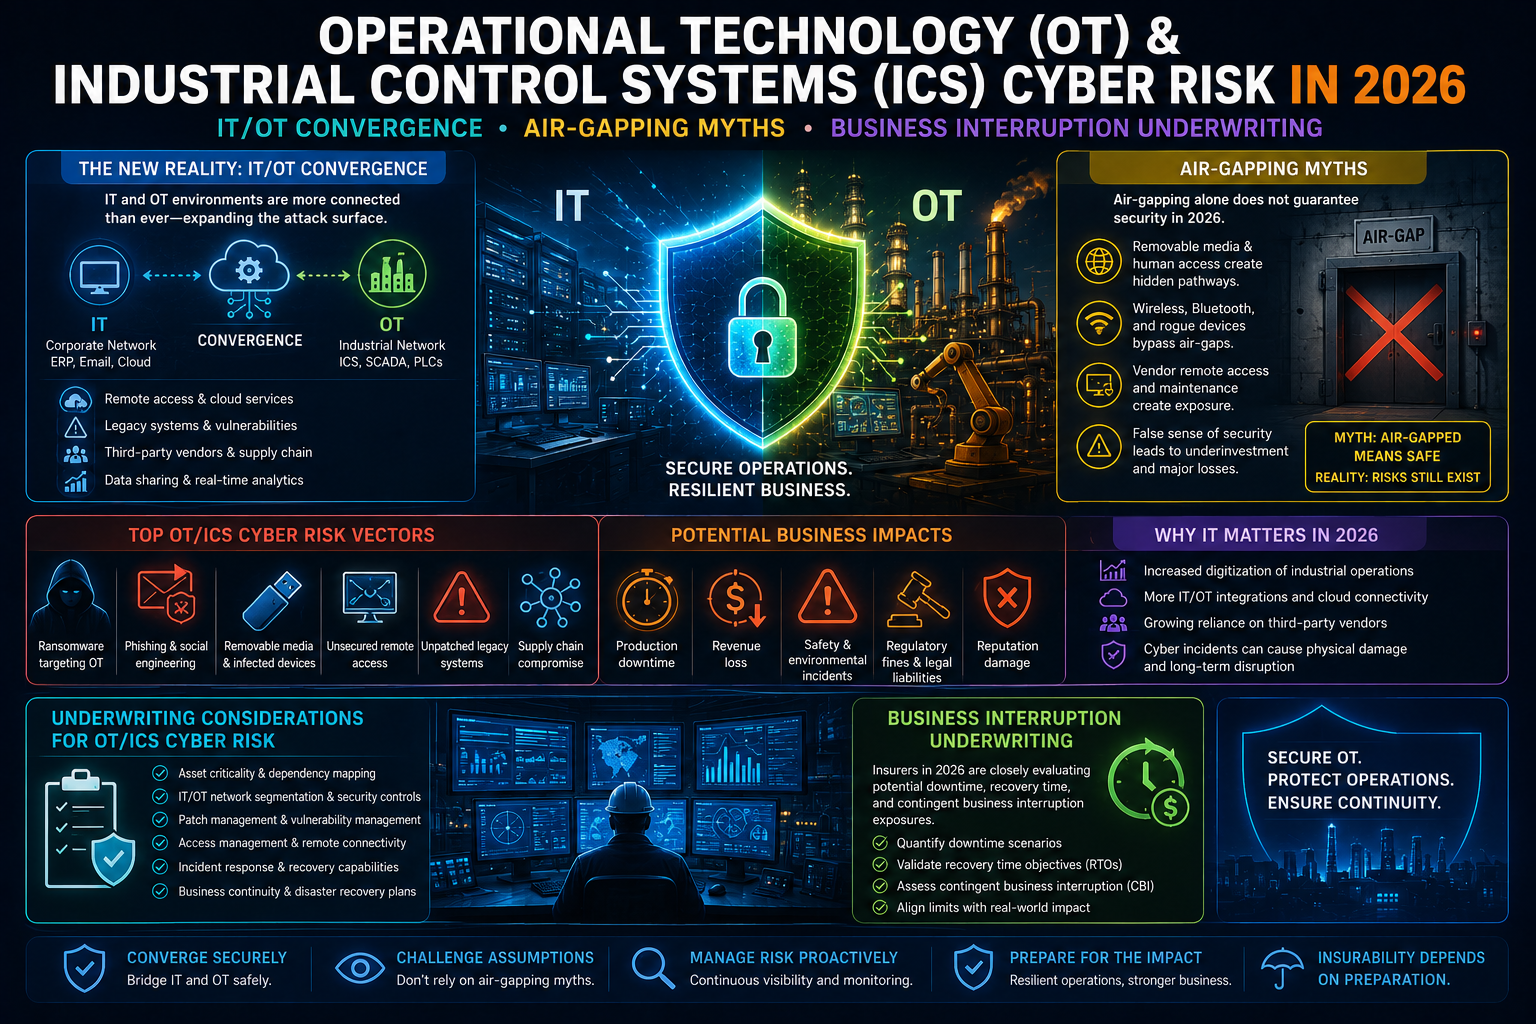
Operational Technology (OT) & Industrial Control Systems (ICS) Cyber Risk in 2026: IT/OT Convergence, Air-Gapping Myths, & Business Interruption Underwriting

Digital representation of industrial control systems, SCADA security, and smart factory network protection.

Published: September 2026 | Technical Risk & Insurance Strategy Guide As manufacturing plants, energy grids, logistics hubs, and critical infrastructure increasingly connect operational technology (OT) and industrial control systems (ICS) to corporate IT networks, the air-gapping defense strategy has become largely obsolete. Threat actors are exploiting converged IT/OT attack surfaces to deploy ransomware, manipulate industrial … Read more

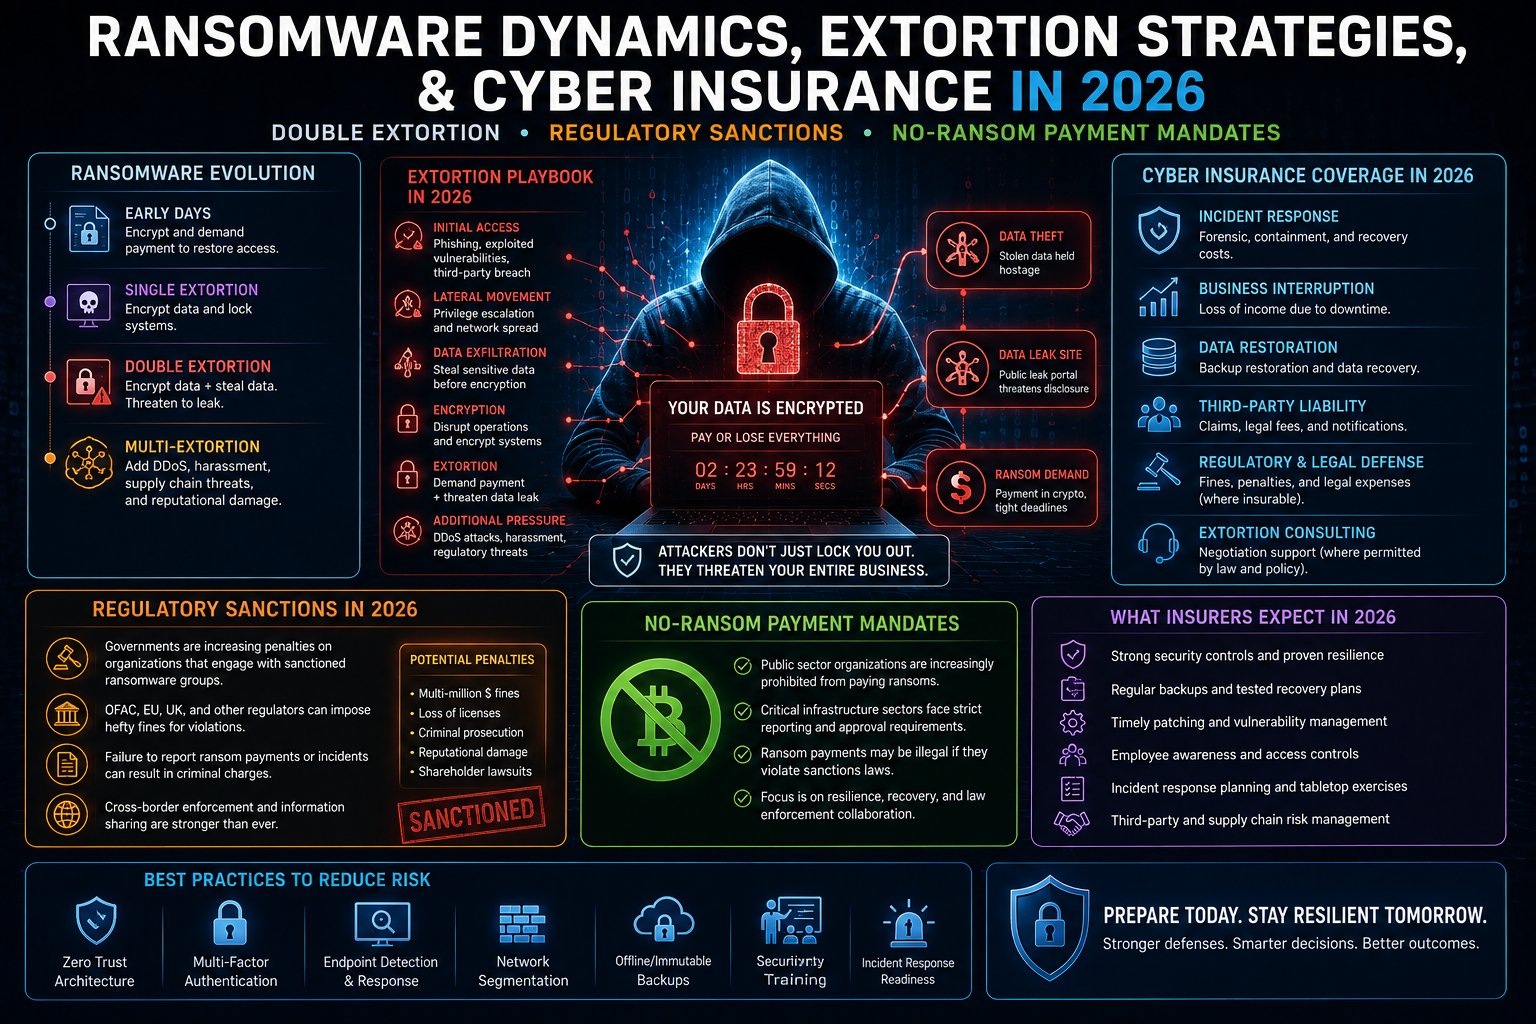
Ransomware Dynamics, Extortion Strategies, & Cyber Insurance in 2026: Double Extortion, Regulatory Sanctions, & No-Ransom Payment Mandates

Conceptual digital artwork representing cyber extortion defense, encrypted data vaults, and ransomware mitigation.

Published: September 2026 | Technical Risk & Insurance Strategy Guide Ransomware has evolved from simple file-encrypting malware into complex, multi-tiered cyber extortion campaigns. Threat actors routinely execute double extortion (encrypting systems while exfiltrating sensitive data) and triple extortion (harassing customers, employees, or regulators directly). Concurrently, legal and regulatory environments have shifted dramatically. Governments and insurance … Read more

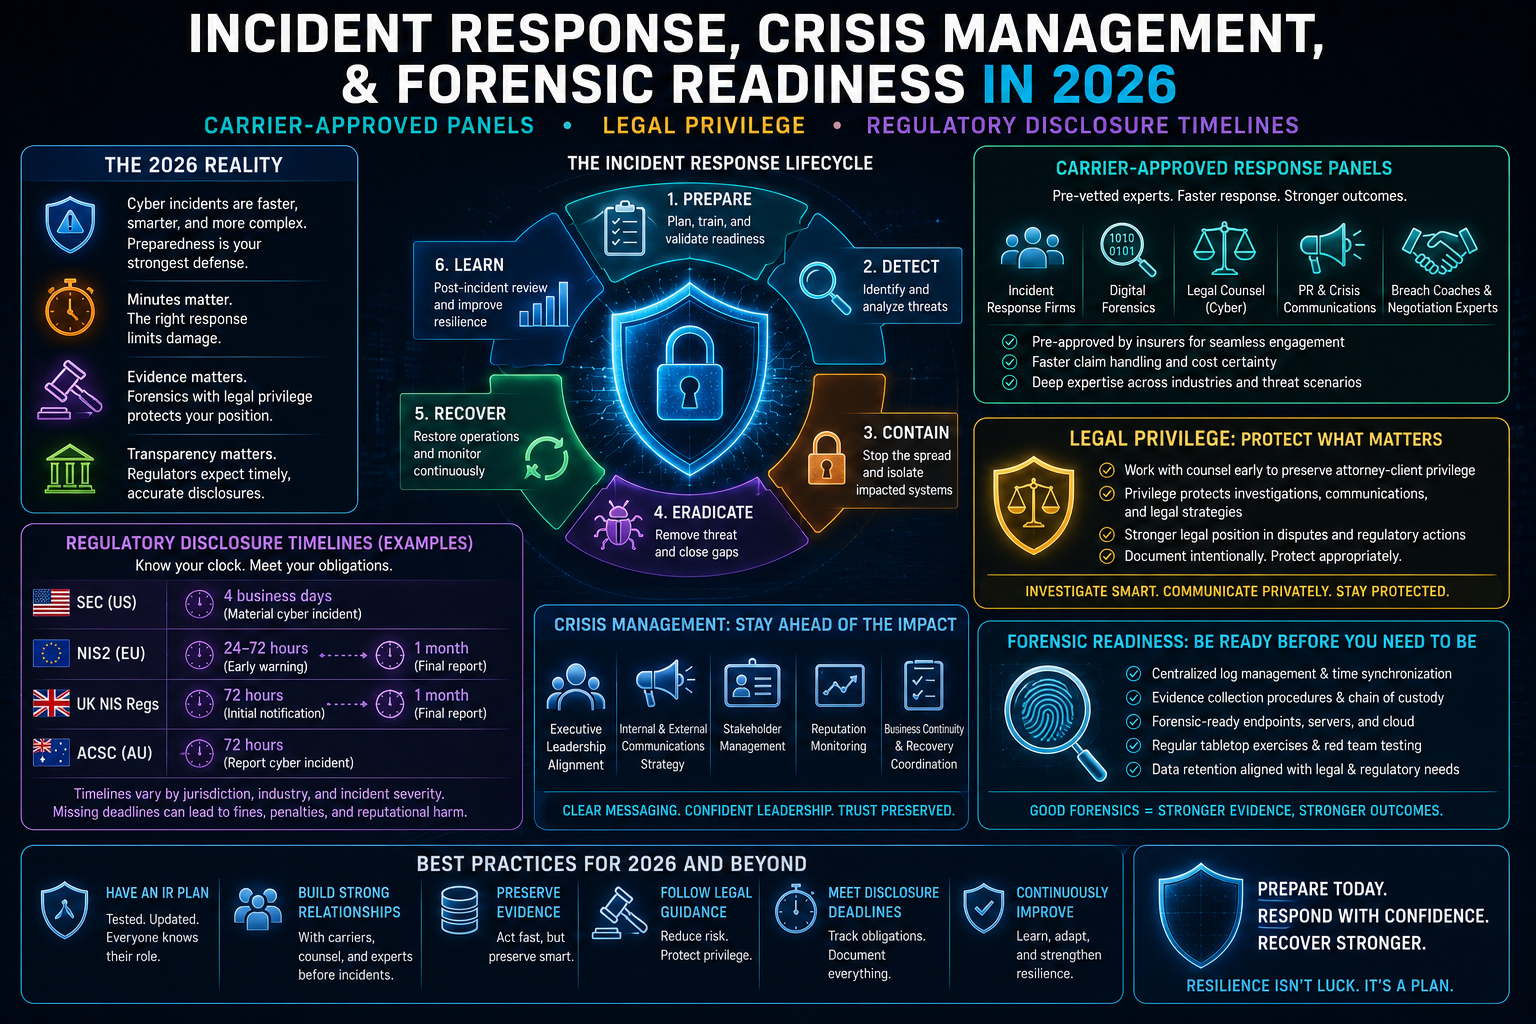
Incident Response, Crisis Management, & Forensic Readiness in 2026: Carrier-Approved Panels, Legal Privilege, & Regulatory Disclosure Timelines

Digital representation of a centralized cyber incident response war room monitoring network threats and legal compliance metrics.

Published: September 2026 | Technical Risk & Insurance Strategy Guide When a major cyber incident strikes, the speed and structure of the initial response dictate both operational recovery and insurance claim approval. Modern cyber insurance policies do not merely function as financial safety nets; they operate as tightly regulated response ecosystems requiring strict adherence to … Read more

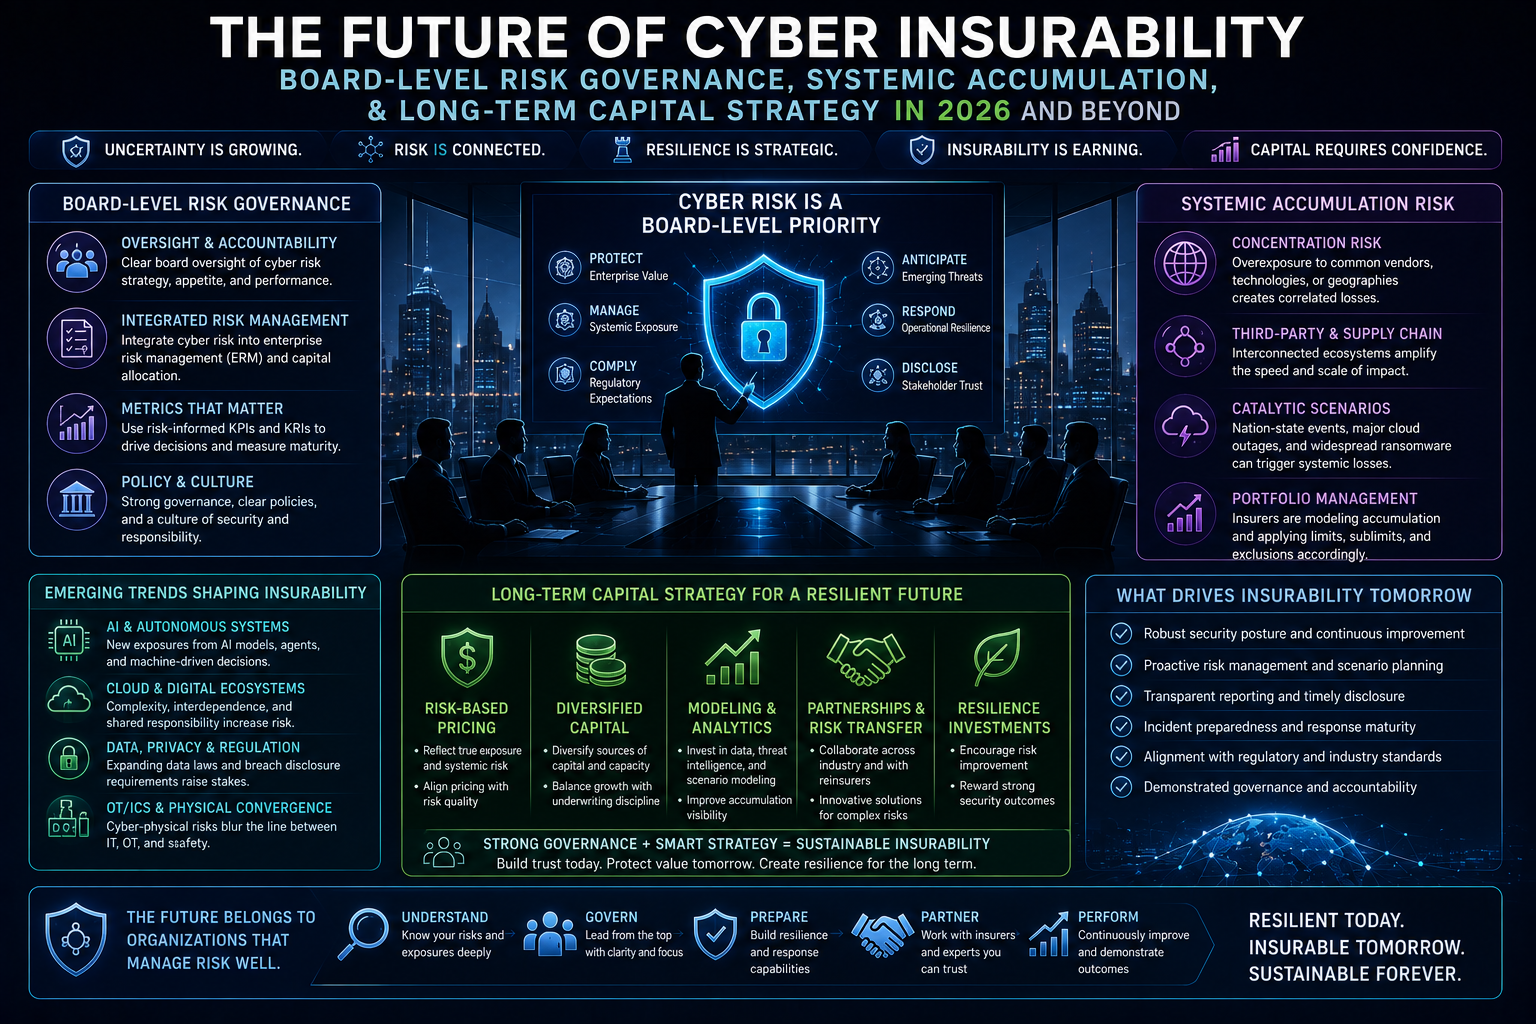
The Future of Cyber Insurability: Board-Level Risk Governance, Systemic Accumulation, & Long-Term Capital Strategy

Conceptual digital visual representing corporate board risk governance, post-quantum cryptography, and global cyber risk strategy.

Published: September 2026 | Technical Risk & Insurance Strategy Guide As cyber threats evolve into systemic, nation-state, and AI-driven risks, cyber insurance has transitioned from a basic risk-transfer product into a strategic benchmark of corporate governance. Insurers no longer evaluate security in isolation; they analyze how executive leadership, board members, and capital allocation frameworks manage … Read more